
C0161
主張
“選擇忽視且不修復 myGovID 的安全漏洞,該漏洞的產生是因為所選擇的驗證協議為客製化設計,不符合標準實務。”
原始來源: Matthew Davis
分析日期: 29 Jan 2026
原始來源
✅ 事實查核
### ### myGovID myGovID 安全漏洞 ān quán lòu dòng - - 驗證碼 yàn zhèng mǎ 重送 zhòng sòng 攻擊 gōng jī
### myGovID Security Vulnerability - Code Replay Attack
該主張 gāi zhǔ zhāng 提及 tí jí myGovID myGovID 存在 cún zài 的 de 真實 zhēn shí 安全漏洞 ān quán lòu dòng 。 。 The claim references a real security vulnerability identified in myGovID.
2024 2024 年 nián 8 8 月 yuè , , 墨爾本 mò ěr běn 大學 dà xué 的 de Ben Ben Frengley Frengley 與 yǔ Thinking Thinking Cybersecurity Cybersecurity 執行長 zhí xíng zhǎng 、 、 澳洲 ào zhōu 國立 guó lì 大學 dà xué 兼任 jiān rèn 教授 jiào shòu Vanessa Vanessa Teague Teague 發現 fā xiàn myGovID myGovID 驗證 yàn zhèng 系統 xì tǒng 存在 cún zài 重大 zhòng dà 漏洞 lòu dòng [ [ 1 1 ] ] 。 。 In August 2024, security researchers Ben Frengley (University of Melbourne) and Vanessa Teague (CEO of Thinking Cybersecurity, ANU adjunct professor) discovered a critical vulnerability in myGovID's authentication system [1].
此 cǐ 漏洞 lòu dòng 為 wèi * * * * 驗證碼 yàn zhèng mǎ 重送 zhòng sòng 攻擊 gōng jī * * * * , , 利用 lì yòng 基本 jī běn 設計 shè jì 缺陷 quē xiàn 運作 yùn zuò 。 。 The vulnerability is a **code replay attack** that exploits a fundamental design flaw.
攻擊者 gōng jī zhě 可 kě 建立 jiàn lì 假網 jiǎ wǎng 站 zhàn 並擷 bìng xié 取 qǔ 使用者 shǐ yòng zhě 電子 diàn zi 郵件 yóu jiàn 地址 dì zhǐ 。 。 An attacker can set up a fake website and capture a user's email address.
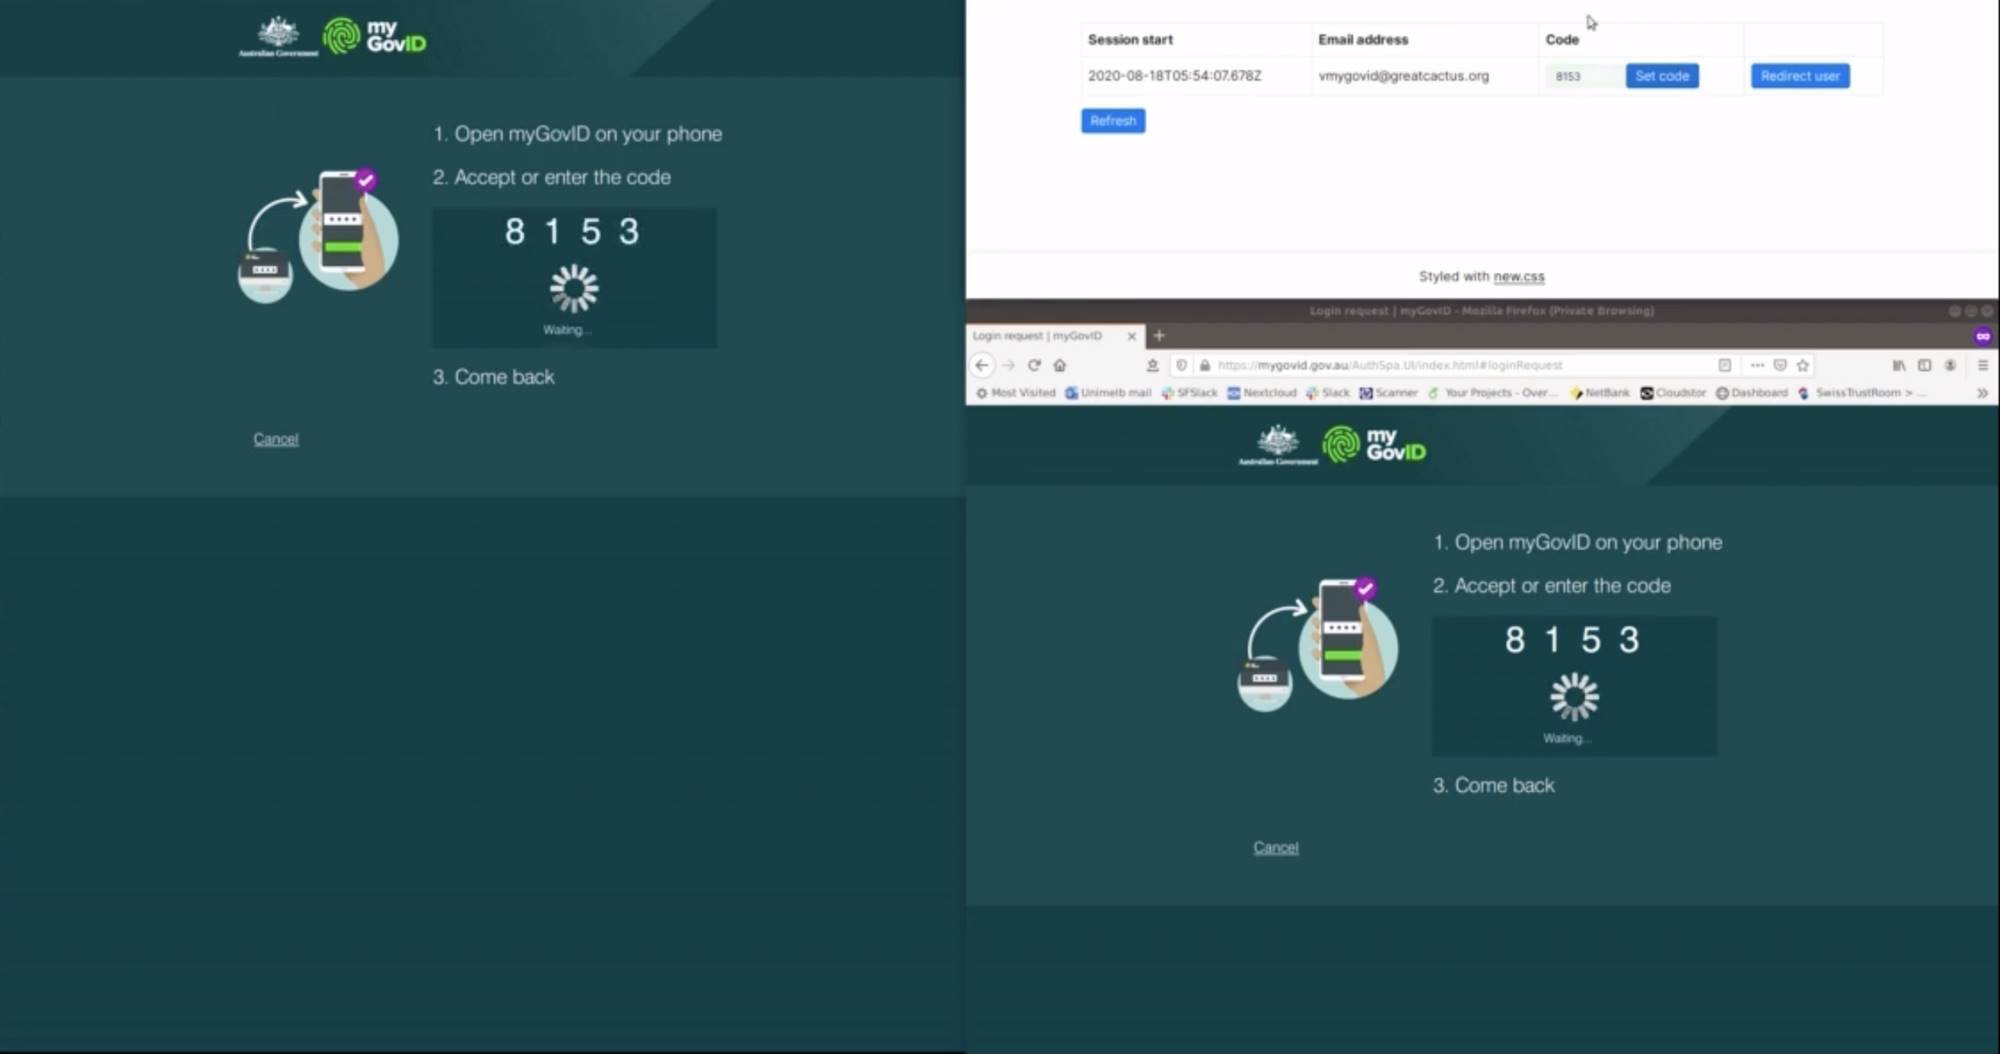
當攻 dāng gōng 擊者 jī zhě 使用 shǐ yòng 受害者 shòu hài zhě 電子 diàn zi 郵件 yóu jiàn 在 zài 合法政府 hé fǎ zhèng fǔ 入口 rù kǒu 網站 wǎng zhàn 啟動驗 qǐ dòng yàn 證時 zhèng shí , , 入口 rù kǒu 網站 wǎng zhàn 會 huì 顯示 xiǎn shì 4 4 位數 wèi shù PIN PIN 碼 mǎ 。 。 When the attacker initiates authentication at a legitimate government portal using the victim's email, the portal displays a 4-digit PIN.
攻擊者 gōng jī zhě 透過 tòu guò 假網 jiǎ wǎng 站 zhàn 將此 jiāng cǐ PIN PIN 碼轉 mǎ zhuǎn 傳給 chuán gěi 受害者 shòu hài zhě , , 當 dāng 受害者 shòu hài zhě 在 zài myGovID myGovID 應用 yīng yòng 程式 chéng shì 中輸入 zhōng shū rù 時 shí , , 便會 biàn huì 在 zài 不知情 bù zhī qíng 的 de 情況 qíng kuàng 下 xià 授予 shòu yǔ 攻擊者 gōng jī zhě 完整 wán zhěng 存取 cún qǔ 合法政府 hé fǎ zhèng fǔ 帳戶 zhàng hù 的 de 權限 quán xiàn 。 。 The attacker relays this PIN to the victim through the fake site, and when the victim enters it into their myGovID app, they unknowingly grant the attacker full access to legitimate government accounts.
一個 yī gè 關鍵 guān jiàn 的 de 設計 shè jì 弱點 ruò diǎn 是 shì myGovID myGovID 應用 yīng yòng 程式 chéng shì * * * * 完全 wán quán 不 bù 顯示 xiǎn shì 是 shì 哪個 nǎ gè 機構 jī gòu 正在 zhèng zài 要求 yāo qiú 驗證 yàn zhèng * * * * [ [ 2 2 ] ] 。 。 A critical design weakness is that the myGovID app provides **no indication of which organization is requesting authentication** [2].
研究 yán jiū 人員 rén yuán 於 yú 2024 2024 年 nián 8 8 月 yuè 19 19 日向 rì xiàng 澳洲 ào zhōu 信號局 xìn hào jú ( ( ASD ASD ) ) 通報 tōng bào 此 cǐ 漏洞 lòu dòng [ [ 3 3 ] ] 。 。 The researchers reported this vulnerability to the Australian Signals Directorate (ASD) on August 19, 2024 [3].
依據業界 yī jù yè jiè 最佳 zuì jiā 實務 shí wù , , 他們 tā men 提出 tí chū 90 90 天 tiān 的 de 負責任 fù zé rèn 揭露 jiē lù 期 qī , , 讓 ràng 政府 zhèng fǔ 有 yǒu 時間 shí jiān 在 zài 公開 gōng kāi 揭露 jiē lù 前開 qián kāi 發並 fā bìng 實施 shí shī 修 xiū 復 fù 方案 fāng àn [ [ 1 1 ] ] 。 。 According to industry best practice, they proposed a 90-day responsible disclosure period to allow the government time to develop and implement a fix before public disclosure [1].
### ### 政府 zhèng fǔ 回應 huí yīng : : 拒絕 jù jué 修 xiū 復 fù ### Government's Response: Refusal to Fix
2024 2024 年 nián 9 9 月 yuè 18 18 日 rì , , 澳洲 ào zhōu 稅務局 shuì wù jú ( ( ATO ATO ) ) 與 yǔ 研究 yán jiū 人員會面 rén yuán huì miàn , , 並明確 bìng míng què 表示 biǎo shì * * * * 「 「 不 bù 打算 dǎ suàn 變 biàn 更 gèng 協議 xié yì 」 」 * * * * [ [ 3 3 ] ] 。 。 On September 18, 2024, the Australian Taxation Office (ATO) met with the researchers and explicitly stated it **"did not intend to change the protocol"** [3].
這 zhè 代表 dài biǎo 政府 zhèng fǔ 拒絕 jù jué 修補此 xiū bǔ cǐ 漏洞 lòu dòng 。 。 This means the government declined to remediate the vulnerability.
此外 cǐ wài , , ATO ATO 將此 jiāng cǐ 漏洞 lòu dòng 定性 dìng xìng 為 wèi 「 「 比較 bǐ jiào 像是 xiàng shì 公眾 gōng zhòng 認知 rèn zhī 問題 wèn tí 」 」 而 ér 非 fēi 需要 xū yào 變 biàn 更 gèng 協議 xié yì 的 de 技術 jì shù 缺陷 quē xiàn [ [ 3 3 ] ] 。 。 Additionally, the ATO characterized the vulnerability as "more of a public awareness issue" rather than a technical flaw requiring protocol changes [3].
ATO ATO 還發表聲 hái fā biǎo shēng 明宣稱 míng xuān chēng myGovID myGovID 「 「 比 bǐ 任何 rèn hé 憑證 píng zhèng 都 dōu 更 gèng 安全 ān quán 」 」 , , 對 duì 研究 yán jiū 人員 rén yuán 的 de 疑慮 yí lǜ 不予 bù yǔ 理會 lǐ huì [ [ 4 4 ] ] 。 。 The ATO also issued statements claiming myGovID was "more secure than any credential," dismissing researcher concerns [4].
在 zài 政府 zhèng fǔ 拒絕 jù jué 修 xiū 復 fù 漏洞 lòu dòng 後 hòu , , 研究 yán jiū 人員 rén yuán 於 yú 2024 2024 年 nián 9 9 月 yuè 21 21 日公 rì gōng 開 kāi 揭露 jiē lù — — — — 在 zài 提出 tí chū 負責任 fù zé rèn 揭露 jiē lù 期 qī 的 de 情況 qíng kuàng 下 xià 仍 réng 發布 fā bù 了 le 他們 tā men 的 de 發現 fā xiàn [ [ 2 2 ] ] 。 。 After the government refused to fix the vulnerability, the researchers went public on September 21, 2024 - publishing their findings despite having proposed a responsible disclosure period [2].
資安 zī ān 研究 yán jiū 人員明確 rén yuán míng què 警告 jǐng gào 大眾 dà zhòng 在 zài 登入 dēng rù 漏洞 lòu dòng 修 xiū 復 fù 前 qián 不要 bú yào 使用 shǐ yòng myGovID myGovID [ [ 1 1 ] ] 。 。 The security researchers explicitly warned the public not to use myGovID until the login flaw was fixed [1].
### ### 監察使 jiān chá shǐ 的 de 佐證 zuǒ zhèng ### Supporting Evidence from Ombudsman
2024 2024 年 nián 8 8 月 yuè , , 澳洲 ào zhōu 監察使 jiān chá shǐ 發布 fā bù 「 「 確保 què bǎo myGov myGov 安全 ān quán 」 」 報告 bào gào , , 指出 zhǐ chū myGov myGov / / myGovID myGovID 系統 xì tǒng 存在 cún zài 多項 duō xiàng 安全 ān quán 缺陷 quē xiàn , , 包括 bāo kuò 不 bù 一致 yí zhì 的 de 身分 shēn fèn 驗證 yàn zhèng 標準 biāo zhǔn 、 、 對 duì 未經 wèi jīng 授權 shòu quán 帳戶 zhàng hù 連結 lián jié 的 de 有限 yǒu xiàn 安全 ān quán 管控 guǎn kòng , , 以及 yǐ jí 詐 zhà 騙者將 piàn zhě jiāng 退休金 tuì xiū jīn 轉移 zhuǎn yí 和 hé 提交 tí jiāo 虛假 xū jiǎ 福利 fú lì 申請 shēn qǐng 的 de 實例 shí lì [ [ 5 5 ] ] 。 。 In August 2024, the Australian Ombudsman published the "Keeping myGov Secure" report, which identified multiple security deficiencies in myGov/myGovID systems, including inconsistent proof-of-identity standards, limited security controls for unauthorized account linking, and instances of fraudsters redirecting pension payments and submitting false benefit claims [5].
澳洲 ào zhōu 服務部 fú wù bù 於 yú 2024 2024 年 nián 7 7 月底 yuè dǐ 同意 tóng yì 這些 zhè xiē 建議 jiàn yì , , 但將 dàn jiāng 實施 shí shī 時間 shí jiān 推遲 tuī chí 至 zhì 2025 2025 年初 nián chū , , 顯示 xiǎn shì 對 duì 緊急 jǐn jí 安全 ān quán 事項 shì xiàng 未 wèi 採取 cǎi qǔ 立即 lì jí 行動 xíng dòng [ [ 5 5 ] ] 。 。 Services Australia agreed to these recommendations in late July 2024 but deferred implementation to early 2025, indicating no immediate action was taken on urgent security matters [5].
缺失的脈絡
### ### 1 1 . . 「 「 客 kè 製 zhì 化 huà 」 」 驗證 yàn zhèng 協議 xié yì 的 de 說 shuō 法正確 fǎ zhèng què
### 1. The "Bespoke" Authentication Protocol is Accurate
該主張 gāi zhǔ zhāng 準確 zhǔn què 地將 dì jiāng myGovID myGovID 的 de 驗證 yàn zhèng 協議 xié yì 描述 miáo shù 為 wèi 非 fēi 標準 biāo zhǔn 協議 xié yì 。 。 The claim accurately characterizes myGovID's authentication protocol as non-standard. myGovID uses the **Trusted Digital Identity Framework (TDIF)**, which is a proprietary, bespoke system specific to Australia - not OpenID Connect, OAuth 2.0, or other internationally recognized standards [6].
myGovID myGovID 使用 shǐ yòng * * * * 可信 kě xìn 數位 shù wèi 身分 shēn fèn 框架 kuāng jià ( ( TDIF TDIF ) ) * * * * , , 這是 zhè shì 澳洲 ào zhōu 專屬 zhuān shǔ 的 de 客 kè 製 zhì 化 huà 系 xì 統 tǒng — — — — 而 ér 非 fēi OpenID OpenID Connect Connect 、 、 OAuth OAuth 2.0 2.0 或 huò 其他 qí tā 國際認 guó jì rèn 可 kě 的 de 標準 biāo zhǔn [ [ 6 6 ] ] 。 。 Security researchers have recommended that the TDIF framework be deprecated and replaced with standard protocols like OpenID Connect [2].
資安 zī ān 研究 yán jiū 人員建議 rén yuán jiàn yì 應 yīng 廢除 fèi chú TDIF TDIF 框架 kuāng jià , , 改採 gǎi cǎi OpenID OpenID Connect Connect 等 děng 標準 biāo zhǔn 協議 xié yì [ [ 2 2 ] ] 。 。 ### 2. Protocol Design vs. Implementation Issues
### ### 2 2 . . 協議 xié yì 設計 shè jì 與 yǔ 實作 shí zuò 問題 wèn tí 的 de 區別 qū bié While the vulnerability exists, there is a technical distinction worth noting: the fundamental flaw appears to stem from the protocol's design (the lack of context about who is requesting authentication in the myGovID app), not necessarily implementation errors.
雖然 suī rán 漏洞 lòu dòng 確實 què shí 存在 cún zài , , 但 dàn 有 yǒu 一個 yī gè 技術區 jì shù qū 別 bié 值得注意 zhí de zhù yì : : 基本 jī běn 缺陷 quē xiàn 似乎 sì hū 源自 yuán zì 協議 xié yì 設計 shè jì ( ( myGovID myGovID 應用 yīng yòng 程式 chéng shì 缺乏 quē fá 關於 guān yú 誰 shuí 正在 zhèng zài 要求 yāo qiú 驗證 yàn zhèng 的 de 上下文 shàng xià wén 資訊 zī xùn ) ) , , 而 ér 不 bù 一定 yí dìng 是 shì 實作 shí zuò 錯誤 cuò wù 。 。 However, this distinction does not diminish the validity of the claim - a flawed protocol design is still a flaw that requires fixing.
然而 rán ér , , 這個 zhè gè 區別 qū bié 並不減 bìng bù jiǎn 損該 sǔn gāi 主張 zhǔ zhāng 的 de 有效性 yǒu xiào xìng — — — — 有 yǒu 缺陷 quē xiàn 的 de 協議 xié yì 設計 shè jì 仍然 réng rán 是 shì 缺陷 quē xiàn , , 需要 xū yào 修 xiū 復 fù 。 。 ### 3. Timeline and Context
### ### 3 3 . . 時間軸 shí jiān zhóu 與 yǔ 背景 bèi jǐng The vulnerability discovery occurred late in the Coalition government's tenure.
漏洞 lòu dòng 發現 fā xiàn 時機 shí jī 接近 jiē jìn Coalition Coalition 政府 zhèng fǔ 任期 rèn qī 尾聲 wěi shēng 。 。 The Coalition was voted out of office in May 2022.
Coalition Coalition 於 yú 2022 2022 年 nián 5 5 月 yuè 卸任 xiè rèn 。 。 The vulnerability was discovered in August 2024 by the Albanese Labor government.
漏洞 lòu dòng 於 yú 2024 2024 年 nián 8 8 月 yuè 由 yóu Albanese Albanese 領導 lǐng dǎo 的 de Labor Labor 政府 zhèng fǔ 時期 shí qī 發現 fā xiàn 。 。 This means:
- The Coalition government (2013-2022) would not have made the September 2024 decision to refuse remediation
- The current (Labor) government inherited myGovID and made the decision not to change the protocol [3]
However, the claim may be referring to the Coalition government's original decision to develop and deploy myGovID using a bespoke, non-standard protocol rather than established industry standards - which would have been a decision made during the Coalition's time in office (2013-2022).
這 zhè 意味著 yì wèi zhù : : - - Coalition Coalition 政府 zhèng fǔ ( ( 2013 2013 - - 2022 2022 ) ) 不 bù 可能 kě néng 做出 zuò chū 2024 2024 年 nián 9 9 月 yuè 拒絕 jù jué 修 xiū 復 fù 的 de 決定 jué dìng - - 現任 xiàn rèn ( ( Labor Labor ) ) 政府 zhèng fǔ 繼承 jì chéng 了 le myGovID myGovID , , 並 bìng 做出 zuò chū 不變 bù biàn 更 gèng 協議 xié yì 的 de 決定 jué dìng [ [ 3 3 ] ] 然而 rán ér , , 該主張 gāi zhǔ zhāng 可能 kě néng 是 shì 指 zhǐ Coalition Coalition 政府 zhèng fǔ 最初 zuì chū 決定 jué dìng 使用 shǐ yòng 客 kè 製 zhì 化 huà 、 、 非標 fēi biāo 準協議 zhǔn xié yì 而 ér 非業界 fēi yè jiè 既定 jì dìng 標準 biāo zhǔn 來 lái 開發 kāi fā 和 hé 部署 bù shǔ myGovID myGovID — — — — 這應 zhè yīng 是 shì Coalition Coalition 執政期 zhí zhèng qī 間 jiān ( ( 2013 2013 - - 2022 2022 ) ) 所 suǒ 做 zuò 的 de 決定 jué dìng 。 。 來源可信度評估
### ### 原始 yuán shǐ 來源 lái yuán : : Thinking Thinking Cybersecurity Cybersecurity
### Original Source: Thinking Cybersecurity
提供 tí gōng 的 de 原始 yuán shǐ 來源 lái yuán ( ( Thinking Thinking Cybersecurity Cybersecurity ) ) 是 shì 由 yóu Vanessa Vanessa Teague Teague 領導 lǐng dǎo 的 de 機構 jī gòu , , 她 tā 是 shì 發現 fā xiàn 該 gāi 漏洞 lòu dòng 的 de 研究 yán jiū 人員 rén yuán 之一 zhī yī 。 。 The original source provided (Thinking Cybersecurity) is an organization led by Vanessa Teague, one of the researchers who discovered the vulnerability.
這創造 zhè chuàng zào 了關 le guān 於 yú 漏洞 lòu dòng 本身 běn shēn 的 de 直接 zhí jiē 來源 lái yuán 。 。 This creates a direct source on the vulnerability itself.
Vanessa Vanessa Teague Teague 具備 jù bèi : : Vanessa Teague is:
- An ANU adjunct professor and security researcher
- A credible academic voice in cybersecurity
- Has published peer-reviewed work on electoral security and digital systems [7]
However, as one of the researchers reporting on their own finding, there is inherent bias in favor of emphasizing the vulnerability's severity.
- - 澳洲 ào zhōu 國立 guó lì 大學 dà xué 兼任 jiān rèn 教授 jiào shòu 及 jí 資安 zī ān 研究 yán jiū 人員 rén yuán 身份 shēn fèn ### Primary Sources on This Issue
- - 網路 wǎng lù 安全 ān quán 領域 lǐng yù 可信 kě xìn 賴的 lài de 學術 xué shù 聲音 shēng yīn The most reliable sources are:
- **Technology news outlets** (iTnews, InnovationAus): Mainstream Australian tech journalism covering the vulnerability discovery and government response [1][3]
- **Government sources** (Ombudsman report, ATO statements): Official documentation of security concerns and government positions [4][5]
- **Security research** (Thinking Cybersecurity, researchers' technical documentation): Academic and professional security analysis [2]
The claim is well-supported by mainstream technology journalism and government reports, not primarily dependent on a single partisan source.
- - 曾 céng 發表關 fā biǎo guān 於 yú 選舉 xuǎn jǔ 安全 ān quán 與 yǔ 數位 shù wèi 系統 xì tǒng 的 de 同儕 tóng chái 審查 shěn chá 研究 yán jiū [ [ 7 7 ] ] 然而 rán ér , , 作為 zuò wèi 報告 bào gào 自身 zì shēn 發現 fā xiàn 的 de 研究 yán jiū 人員 rén yuán 之一 zhī yī , , 存在 cún zài 強調 qiáng diào 漏洞 lòu dòng 嚴重性 yán zhòng xìng 的 de 固有 gù yǒu 偏見 piān jiàn 。 。 ### ### 此議題 cǐ yì tí 的 de 主要 zhǔ yào 來源 lái yuán 最 zuì 可靠 kě kào 的 de 來源 lái yuán 包括 bāo kuò : : - - * * * * 科技 kē jì 新聞 xīn wén 媒體 méi tǐ * * * * ( ( iTnews iTnews 、 、 InnovationAus InnovationAus ) ) : : 報導 bào dǎo 漏洞 lòu dòng 發現 fā xiàn 與 yǔ 政府 zhèng fǔ 回應 huí yīng 的 de 澳洲 ào zhōu 主流 zhǔ liú 科技 kē jì 新聞 xīn wén [ [ 1 1 ] ] [ [ 3 3 ] ] - - * * * * 政府 zhèng fǔ 來源 lái yuán * * * * ( ( 監察使 jiān chá shǐ 報告 bào gào 、 、 ATO ATO 聲明 shēng míng ) ) : : 安全 ān quán 疑慮 yí lǜ 與 yǔ 政府 zhèng fǔ 立場 lì chǎng 的 de 官方 guān fāng 文件 wén jiàn [ [ 4 4 ] ] [ [ 5 5 ] ] - - * * * * 資安 zī ān 研究 yán jiū * * * * ( ( Thinking Thinking Cybersecurity Cybersecurity 、 、 研究 yán jiū 人員技術 rén yuán jì shù 文件 wén jiàn ) ) : : 學術 xué shù 與 yǔ 專業 zhuān yè 資安 zī ān 分析 fēn xī [ [ 2 2 ] ] 該主張 gāi zhǔ zhāng 獲得 huò dé 主流 zhǔ liú 科技 kē jì 新聞 xīn wén 與 yǔ 政府 zhèng fǔ 報告 bào gào 的 de 充分 chōng fèn 支持 zhī chí , , 而 ér 非 fēi 主要 zhǔ yào 依賴 yī lài 單一黨 dān yī dǎng 派 pài 來源 lái yuán 。 。 ⚖️
Labor 比較
### ### Labor Labor 是否 shì fǒu 採用類 cǎi yòng lèi 似的 shì de 客 kè 製 zhì 化 huà 驗 yàn 證 zhèng 方式 fāng shì ? ?
### Did Labor Adopt Similar Bespoke Authentication Approaches?
Labor Labor 在 zài myGovID myGovID 開發時 kāi fā shí 並未 bìng wèi 執政 zhí zhèng ( ( Coalition Coalition 執政 zhí zhèng 於 yú 2013 2013 - - 2022 2022 ) ) 。 。 Labor was not in government when myGovID was developed (Coalition governed 2013-2022).
Labor Labor 政府 zhèng fǔ 於 yú 2022 2022 年 nián 5 5 月 yuè 上任 shàng rèn 時繼承 shí jì chéng 了 le myGovID myGovID 系統 xì tǒng 。 。 The Labor government inherited the myGovID system when they took office in May 2022.
**However**, the more relevant comparison is: **How did Labor respond to the discovered vulnerability?**
As noted above, the decision to "not intend to change the protocol" in September 2024 was made by the **Labor government's ATO**, not the Coalition.
* * * * 然而 rán ér * * * * , , 更具 gèng jù 相關性 xiāng guān xìng 的 de 比 bǐ 較 jiào 是 shì : : * * * * Labor Labor 如何 rú hé 回應 huí yīng 已 yǐ 發現 fā xiàn 的 de 漏洞 lòu dòng ? ? This indicates both governments (Coalition for original development, Labor for response to the discovered vulnerability) made questionable cybersecurity decisions regarding myGovID.
* * * * ### Labor's Approach to Digital Identity
如上所述 rú shàng suǒ shù , , 2024 2024 年 nián 9 9 月 yuè 「 「 不 bù 打算 dǎ suàn 變 biàn 更 gèng 協議 xié yì 」 」 的 de 決定 jué dìng 是 shì 由 yóu * * * * Labor Labor 政府 zhèng fǔ 的 de ATO ATO * * * * 做出 zuò chū , , 而 ér 非 fēi Coalition Coalition 。 。 Labor has pursued continued development of myGovID (rebranded as "myID" in November 2024) under a digital identity scheme.
這顯示 zhè xiǎn shì 兩個 liǎng gè 政府 zhèng fǔ ( ( Coalition Coalition 負責 fù zé 最初 zuì chū 開發 kāi fā , , Labor Labor 負責 fù zé 對 duì 已 yǐ 發現 fā xiàn 漏洞 lòu dòng 的 de 回應 huí yīng ) ) 在 zài myGovID myGovID 的 de 資安 zī ān 決策 jué cè 上 shàng 都 dōu 有 yǒu 可議 kě yì 之處 zhī chù 。 。 Labor has not abandoned the bespoke TDIF framework but instead continued operating within it [8].
### ### Labor Labor 的 de 數位 shù wèi 身分 shēn fèn 政策 zhèng cè 方針 fāng zhēn This suggests Labor may bear some responsibility for not addressing the architectural vulnerability once it was discovered under their watch.
Labor Labor 持續 chí xù 推動 tuī dòng myGovID myGovID 的 de 開發 kāi fā ( ( 於 yú 2024 2024 年 nián 11 11 月 yuè 重新命名 chóng xīn mìng míng 為 wèi 「 「 myID myID 」 」 ) ) , , 納入 nà rù 數位 shù wèi 身分 shēn fèn 計畫 jì huà 。 。 Labor Labor 並未放棄 bìng wèi fàng qì 客 kè 製 zhì 化 huà 的 de TDIF TDIF 框架 kuāng jià , , 而是 ér shì 繼續 jì xù 在 zài 該 gāi 框架 kuāng jià 內運作 nèi yùn zuò [ [ 8 8 ] ] 。 。 這顯示 zhè xiǎn shì Labor Labor 在 zài 發現 fā xiàn 架構 jià gòu 漏洞 lòu dòng 後 hòu 可能 kě néng 也 yě 負有 fù yǒu 未 wèi 處理 chù lǐ 的 de 責任 zé rèn 。 。 🌐
平衡觀點
### ### Coalition Coalition 的 de 設計 shè jì 決定 jué dìng ( ( 2013 2013 - - 2022 2022 ) )
### The Coalition's Design Decision (2013-2022)
當 dāng Coalition Coalition 政府 zhèng fǔ 決定 jué dìng 使用 shǐ yòng 專屬 zhuān shǔ 客 kè 製 zhì 化 huà 驗 yàn 證 zhèng 協 xié 議 yì ( ( TDIF TDIF ) ) 而 ér 非 fēi 採用 cǎi yòng OpenID OpenID Connect Connect 等 děng 國際 guó jì 標準 biāo zhǔn 協議 xié yì 來 lái 開發 kāi fā myGovID myGovID 時 shí , , 這 zhè 代表 dài biǎo 一個 yī gè 有 yǒu 疑慮 yí lǜ 的 de 架構 jià gòu 決定 jué dìng 。 。 When the Coalition government decided to develop myGovID using a proprietary, bespoke authentication protocol (TDIF) rather than adopting internationally standard protocols like OpenID Connect, this represented a questionable architectural decision.
選擇 xuǎn zé 此 cǐ 方案 fāng àn 的 de 可能 kě néng 原因 yuán yīn 包括 bāo kuò : : The reasons for this choice were likely:
- Desire for a uniquely Australian solution tailored to specific government needs
- Potential national sovereignty concerns (not relying on international standards)
- Perceived control over the system's security and operations
However, security experts argue that bespoke authentication systems are inherently riskier because they:
- Have limited external security review compared to widely-used standards
- Don't benefit from years of community vulnerability discovery and patching
- Increase the chance of design flaws like the one discovered in 2024 [2]
**Standard security practice is to use proven, widely-audited protocols unless there is a compelling reason not to.**
- - 希望 xī wàng 打造 dǎ zào 獨特 dú tè 符合 fú hé 澳洲 ào zhōu 政府 zhèng fǔ 特定 tè dìng 需求 xū qiú 的 de 解決 jiě jué 方案 fāng àn ### The Government's Response to the Discovered Vulnerability
- - 潛在 qián zài 的國 de guó 家主 jiā zhǔ 權 quán 考量 kǎo liáng ( ( 不依 bù yī 賴國際 lài guó jì 標準 biāo zhǔn ) ) More problematic than the original design choice was the response when the vulnerability was discovered:
**During Coalition government (2013-2022):**
- The Coalition would have deployed and operated myGovID but the vulnerability wasn't discovered until 2024 (after their loss of office)
**During Labor government (September 2024 onward):**
- The ATO explicitly refused to fix the known vulnerability, stating they "did not intend to change the protocol"
- The government dismissed it as a "public awareness issue" rather than a technical design flaw
- No remediation timeline or plan was announced
- The system continued to operate with the known vulnerability
- - 認為 rèn wèi 能 néng 掌控 zhǎng kòng 系統 xì tǒng 安全 ān quán 與 yǔ 運作 yùn zuò ### Expert and Institutional Perspectives
然而 rán ér , , 資安 zī ān 專家 zhuān jiā 認為 rèn wèi 客 kè 製 zhì 化 huà 驗 yàn 證 zhèng 系 xì 統 tǒng 本 běn 質 zhì 上 shàng 風 fēng 險 xiǎn 更 gèng 高 gāo , , 因為 yīn wèi : : The Ombudsman's report reinforces that myGov/myGovID security is inadequate, with the government only agreeing to address deficiencies in 2025 [5].
- - 與 yǔ 廣泛 guǎng fàn 使用 shǐ yòng 的 de 標準 biāo zhǔn 相比 xiāng bǐ , , 外部 wài bù 安全 ān quán 審查 shěn chá 有限 yǒu xiàn The timing suggests this was reactive rather than proactive security governance.
- - 無法 wú fǎ 受益 shòu yì 於 yú 多年 duō nián 社群 shè qún 漏洞 lòu dòng 發現 fā xiàn 與 yǔ 修補 xiū bǔ 的 de 經驗 jīng yàn ### Comparative Government Practice
- - 增加 zēng jiā 如 rú 2024 2024 年 nián 發現 fā xiàn 的 de 設計 shè jì 缺陷 quē xiàn 機率 jī lǜ [ [ 2 2 ] ] Ignoring known security vulnerabilities in authentication systems is not standard practice across responsible governments.
* * * * 標準 biāo zhǔn 資安實務 zī ān shí wù 是 shì 使用 shǐ yòng 經過 jīng guò 驗證 yàn zhèng 、 、 廣泛 guǎng fàn 審查 shěn chá 的 de 協議 xié yì , , 除非 chú fēi 有 yǒu 令人信服 lìng rén xìn fú 的 de 理由 lǐ yóu 不 bù 這麼 zhè me 做 zuò 。 。 The standard industry approach is:
1.
* * * * Acknowledge the vulnerability
2.
### ### 政府 zhèng fǔ 對 duì 已 yǐ 發現 fā xiàn 漏洞 lòu dòng 的 de 回應 huí yīng Develop a remediation plan
3.
比 bǐ 最初 zuì chū 設計 shè jì 選擇 xuǎn zé 更 gèng 有 yǒu 問題 wèn tí 的 de 是 shì 發現 fā xiàn 漏洞 lòu dòng 後 hòu 的 de 回應 huí yīng : : Implement the fix within a reasonable timeframe
4.
* * * * Coalition Coalition 政府 zhèng fǔ 時期 shí qī ( ( 2013 2013 - - 2022 2022 ) ) : : * * * * Publicly communicate the resolution
The Australian government's response (refusing to fix the protocol design flaw) falls short of these standards.
**Key context:** Neither the Coalition nor Labor has demonstrated strong cybersecurity governance regarding myGovID.
- - Coalition Coalition 部署 bù shǔ 並運作 bìng yùn zuò myGovID myGovID , , 但 dàn 漏洞 lòu dòng 直到 zhí dào 2024 2024 年 nián 才 cái 發現 fā xiàn ( ( 在 zài 他們 tā men 卸任 xiè rèn 後 hòu ) ) The Coalition created a system using non-standard protocols, and Labor (which inherited it) refused to fix it when vulnerabilities were discovered.
* * * * Labor Labor 政府 zhèng fǔ 時期 shí qī ( ( 2024 2024 年 nián 9 9 月 yuè 起 qǐ ) ) : : * * * * Both decisions appear driven by bureaucratic inertia and unwillingness to acknowledge systemic architectural failures.
- - ATO ATO 明確 míng què 拒絕 jù jué 修 xiū 復 fù 已知 yǐ zhī 漏洞 lòu dòng , , 表示 biǎo shì 他們 tā men 「 「 不 bù 打算 dǎ suàn 變 biàn 更 gèng 協議 xié yì 」 」 - - 政府 zhèng fǔ 將其視 jiāng qí shì 為 wèi 「 「 公眾 gōng zhòng 認知 rèn zhī 問題 wèn tí 」 」 而 ér 非技術 fēi jì shù 設計 shè jì 缺陷 quē xiàn - - 未 wèi 公布 gōng bù 修 xiū 復 fù 時間 shí jiān 表 biǎo 或 huò 計畫 jì huà - - 系統 xì tǒng 在 zài 已知 yǐ zhī 漏洞 lòu dòng 存在 cún zài 的 de 情況 qíng kuàng 下 xià 繼續 jì xù 運作 yùn zuò ### ### 專家 zhuān jiā 與 yǔ 機構 jī gòu 觀點 guān diǎn 監察使 jiān chá shǐ 的 de 報告 bào gào 強化 qiáng huà 指出 zhǐ chū myGov myGov / / myGovID myGovID 安全性 ān quán xìng 不足 bù zú , , 政府 zhèng fǔ 僅 jǐn 同意 tóng yì 於 yú 2025 2025 年 nián 處理 chù lǐ 這些 zhè xiē 缺陷 quē xiàn [ [ 5 5 ] ] 。 。 時間點 shí jiān diǎn 顯示 xiǎn shì 這是 zhè shì 反應式 fǎn yīng shì 而 ér 非主動式 fēi zhǔ dòng shì 的 de 安全 ān quán 治理 zhì lǐ 。 。 ### ### 政府 zhèng fǔ 實務比 shí wù bǐ 較 jiào 忽視 hū shì 已知 yǐ zhī 的 de 驗證 yàn zhèng 系統 xì tǒng 安全漏洞 ān quán lòu dòng 並非 bìng fēi 負責任 fù zé rèn 政府 zhèng fǔ 的 de 標準 biāo zhǔn 實務 shí wù 。 。 標準 biāo zhǔn 業界 yè jiè 作法 zuò fǎ 是 shì : : 1 1 . . 承認 chéng rèn 漏洞 lòu dòng 存在 cún zài 2 2 . . 制定 zhì dìng 修 xiū 復 fù 計畫 jì huà 3 3 . . 在 zài 合理 hé lǐ 時間 shí jiān 內 nèi 實施 shí shī 修 xiū 復 fù 4 4 . . 公開溝 gōng kāi gōu 通解 tōng jiě 決 jué 方案 fāng àn 澳洲 ào zhōu 政府 zhèng fǔ 的 de 回應 huí yīng ( ( 拒絕 jù jué 修 xiū 復 fù 協議 xié yì 設計 shè jì 缺陷 quē xiàn ) ) 未達 wèi dá 這些 zhè xiē 標準 biāo zhǔn 。 。 * * * * 重要 zhòng yào 背景 bèi jǐng : : * * * * Coalition Coalition 與 yǔ Labor Labor 在 zài myGovID myGovID 的 de 資安 zī ān 治理 zhì lǐ 上 shàng 都 dōu 未展 wèi zhǎn 現強 xiàn qiáng 有力 yǒu lì 的 de 表現 biǎo xiàn 。 。 Coalition Coalition 使用 shǐ yòng 非標 fēi biāo 準協議 zhǔn xié yì 創建系統 chuàng jiàn xì tǒng , , 而 ér Labor Labor ( ( 繼承該 jì chéng gāi 系統 xì tǒng ) ) 在 zài 發現 fā xiàn 漏洞 lòu dòng 時拒 shí jù 絕修 jué xiū 復 fù 。 。 兩個 liǎng gè 決定 jué dìng 似乎 sì hū 都 dōu 源 yuán 於 yú 官僚 guān liáo 惰性 duò xìng 以及 yǐ jí 不願 bù yuàn 承 chéng 認系 rèn xì 統性 tǒng xìng 架構 jià gòu 失敗 shī bài 。 。 真實
7.0
/ 10
該主 gāi zhǔ 張關 zhāng guān 於 yú myGovID myGovID 漏洞 lòu dòng 及 jí 政府 zhèng fǔ 拒絕 jù jué 修 xiū 復 fù 的 de 事實 shì shí 描述 miáo shù 準確 zhǔn què 。 。
The claim is factually accurate regarding the myGovID vulnerability and the government's refusal to fix it.
然而 rán ér , , 有 yǒu 一個 yī gè 重要 zhòng yào 的 de * * * * 時間 shí jiān 澄清 chéng qīng * * * * : : 拒絕 jù jué 修 xiū 復 fù 的 de 決定 jué dìng 是 shì 由 yóu * * * * 2024 2024 年 nián 9 9 月 yuè 的 de Labor Labor 政府 zhèng fǔ * * * * 做出 zuò chū , , 而 ér 非 fēi Coalition Coalition 政府 zhèng fǔ 。 。 However, there is an important **temporal clarification**: The decision to refuse remediation was made by the **Labor government in September 2024**, not the Coalition government.
Coalition Coalition ( ( 2013 2013 - - 2022 2022 ) ) 做出 zuò chū 最初 zuì chū 使用 shǐ yòng 客 kè 製 zhì 化 huà 、 、 非標 fēi biāo 準協議 zhǔn xié yì 的 de 決定 jué dìng , , 這個 zhè gè 架構 jià gòu 選擇 xuǎn zé 才 cái 導致 dǎo zhì 了 le 此 cǐ 漏洞 lòu dòng 。 。 The Coalition (2013-2022) made the original decision to use a bespoke, non-standard protocol, which was the architectural choice that enabled this vulnerability.
該主張 gāi zhǔ zhāng 可以 kě yǐ 有 yǒu 兩種 liǎng zhǒng 解讀 jiě dú 方式 fāng shì : : The claim could be interpreted two ways:
1. **If referring to original protocol design (Coalition era 2013-2022):** TRUE - The Coalition chose a bespoke protocol over proven standards
2. **If referring to the 2024 refusal to fix the discovered vulnerability:** TRUE but made by Labor government, not Coalition
The statement "Chose to ignore and not fix" most naturally reads as referring to the refusal to remediate after discovery (September 2024), which was a Labor government decision, though the underlying architectural choice was made by the Coalition.
1 1 . . * * * * 若指 ruò zhǐ 最初 zuì chū 協議 xié yì 設計 shè jì ( ( Coalition Coalition 時期 shí qī 2013 2013 - - 2022 2022 ) ) : : * * * * TRUE TRUE - - Coalition Coalition 選擇 xuǎn zé 客 kè 製 zhì 化 huà 協 xié 議 yì 而 ér 非 fēi 成熟 chéng shú 標準 biāo zhǔn 2 2 . . * * * * 若指 ruò zhǐ 2024 2024 年 nián 拒絕 jù jué 修 xiū 復 fù 已 yǐ 發現 fā xiàn 漏洞 lòu dòng : : * * * * TRUE TRUE 但 dàn 由 yóu Labor Labor 政府 zhèng fǔ 做出 zuò chū , , 而 ér 非 fēi Coalition Coalition 「 「 選擇 xuǎn zé 忽視且 hū shì qiě 不修 bù xiū 復 fù 」 」 這句 zhè jù 話 huà 最 zuì 自然 zì rán 地解讀 dì jiě dú 為 wèi 指發 zhǐ fā 現後拒 xiàn hòu jù 絕修 jué xiū 復 fù ( ( 2024 2024 年 nián 9 9 月 yuè ) ) , , 這是 zhè shì Labor Labor 政府 zhèng fǔ 的 de 決定 jué dìng , , 但底 dàn dǐ 層架構 céng jià gòu 選擇 xuǎn zé 是 shì 由 yóu Coalition Coalition 做出 zuò chū 。 。 最終分數
7.0
/ 10
真實
該主 gāi zhǔ 張關 zhāng guān 於 yú myGovID myGovID 漏洞 lòu dòng 及 jí 政府 zhèng fǔ 拒絕 jù jué 修 xiū 復 fù 的 de 事實 shì shí 描述 miáo shù 準確 zhǔn què 。 。
The claim is factually accurate regarding the myGovID vulnerability and the government's refusal to fix it.
然而 rán ér , , 有 yǒu 一個 yī gè 重要 zhòng yào 的 de * * * * 時間 shí jiān 澄清 chéng qīng * * * * : : 拒絕 jù jué 修 xiū 復 fù 的 de 決定 jué dìng 是 shì 由 yóu * * * * 2024 2024 年 nián 9 9 月 yuè 的 de Labor Labor 政府 zhèng fǔ * * * * 做出 zuò chū , , 而 ér 非 fēi Coalition Coalition 政府 zhèng fǔ 。 。 However, there is an important **temporal clarification**: The decision to refuse remediation was made by the **Labor government in September 2024**, not the Coalition government.
Coalition Coalition ( ( 2013 2013 - - 2022 2022 ) ) 做出 zuò chū 最初 zuì chū 使用 shǐ yòng 客 kè 製 zhì 化 huà 、 、 非標 fēi biāo 準協議 zhǔn xié yì 的 de 決定 jué dìng , , 這個 zhè gè 架構 jià gòu 選擇 xuǎn zé 才 cái 導致 dǎo zhì 了 le 此 cǐ 漏洞 lòu dòng 。 。 The Coalition (2013-2022) made the original decision to use a bespoke, non-standard protocol, which was the architectural choice that enabled this vulnerability.
該主張 gāi zhǔ zhāng 可以 kě yǐ 有 yǒu 兩種 liǎng zhǒng 解讀 jiě dú 方式 fāng shì : : The claim could be interpreted two ways:
1. **If referring to original protocol design (Coalition era 2013-2022):** TRUE - The Coalition chose a bespoke protocol over proven standards
2. **If referring to the 2024 refusal to fix the discovered vulnerability:** TRUE but made by Labor government, not Coalition
The statement "Chose to ignore and not fix" most naturally reads as referring to the refusal to remediate after discovery (September 2024), which was a Labor government decision, though the underlying architectural choice was made by the Coalition.
1 1 . . * * * * 若指 ruò zhǐ 最初 zuì chū 協議 xié yì 設計 shè jì ( ( Coalition Coalition 時期 shí qī 2013 2013 - - 2022 2022 ) ) : : * * * * TRUE TRUE - - Coalition Coalition 選擇 xuǎn zé 客 kè 製 zhì 化 huà 協 xié 議 yì 而 ér 非 fēi 成熟 chéng shú 標準 biāo zhǔn 2 2 . . * * * * 若指 ruò zhǐ 2024 2024 年 nián 拒絕 jù jué 修 xiū 復 fù 已 yǐ 發現 fā xiàn 漏洞 lòu dòng : : * * * * TRUE TRUE 但 dàn 由 yóu Labor Labor 政府 zhèng fǔ 做出 zuò chū , , 而 ér 非 fēi Coalition Coalition 「 「 選擇 xuǎn zé 忽視且 hū shì qiě 不修 bù xiū 復 fù 」 」 這句 zhè jù 話 huà 最 zuì 自然 zì rán 地解讀 dì jiě dú 為 wèi 指發 zhǐ fā 現後拒 xiàn hòu jù 絕修 jué xiū 復 fù ( ( 2024 2024 年 nián 9 9 月 yuè ) ) , , 這是 zhè shì Labor Labor 政府 zhèng fǔ 的 de 決定 jué dìng , , 但底 dàn dǐ 層架構 céng jià gòu 選擇 xuǎn zé 是 shì 由 yóu Coalition Coalition 做出 zuò chū 。 。 📚 來源與引用 (8)
-
1
itnews.com.au
ATO declines to change protocol.
iTnews -
2
thinkingcybersecurity.com
Thinkingcybersecurity
-
3
innovationaus.com
Innovationaus
-
4
accountantsdaily.com.au
From security concerns to clashes with workplace policies, the transition to myGovID has caused a few headaches within the profession, but the ATO believes worries are misplaced.
Accountantsdaily Com -
5PDF
Keeping myGov Secure
Ombudsman Gov • PDF Document -
6
architecture.digital.gov.au
Architecture Digital Gov
-
7
cecs.anu.edu.au
Cecs Anu Edu
-
8
ato.gov.au
Ato Gov
評分量表方法論
1-3: 虛假
事實不正確或惡意捏造。
4-6: 部分
有部分真實性,但缺乏或扭曲了背景。
7-9: 大致屬實
微小的技術性問題或措辭問題。
10: 準確
完美驗證且在情境上公正。
方法論: 評分通過交叉比對官方政府記錄、獨立事實查核組織和原始來源文件來確定。